
Monitor your organisation's attack surface, through the adversary's eyes
STFC built the Jashnvareh platform, an integrated External Attack Surface Management (EASM) system, to deliver in under an hour a report that normally takes more than three months and a team of specialists.
Silent Ping: our own console for measuring connectivity- minutes to set up
- 15
- security tests
- 500+
- coverage areas
- 12
- DNS
- TLS / HTTPS
- Certificate Transparency
- BGP · ASN
- RPKI
- SPF · DKIM · DMARC
- Security Headers · CSP
- CORS
- APK / XAPK
- Subdomain Discovery
- Infra Pivot
- Kill-Chain
- Setup to first run
- 15minutes
- Passive assessment
- 20minutes
- Active, in-depth assessment
- 90minutes
- Security tests and checks per assessment
- 500+tests
- Coverage areas, from DNS to mobile apps
- 12domains
- Technical and executive report
- 70+pages
Two small weaknesses, one large loss
Neither weakness looks critical on its own. Scroll to see how an attacker chains them together.
A domain without DMARC
The organisation's domain publishes no enforcement policy. Receiving servers cannot tell a real message from a forged one.
An email from the “CEO”
The attacker sends a message from the chief executive's real address, asking finance to review an urgent invoice. It passes every visual check.
One click on a familiar page
The link opens a page that looks harmless. Underneath it, the company's own payment panel is loaded in an invisible frame.
The click lands somewhere else
The employee clicks “View invoice”. The click actually reaches “Confirm transfer” in the hidden panel, using their own active session.
The consequences
Money has left the account, and the same mailbox is used to reach the next victim. No malware was involved and no server was hacked.
One DNS record and one header would have broken this chain
The platform reports both weaknesses in a passive assessment, in under 20 minutes, and shows how they connect.
_dmarc → p=reject · Content-Security-Policy: frame-ancestors 'none'
What your organisation sees in the platform
The images below are from the real Jashnvareh platform interface.
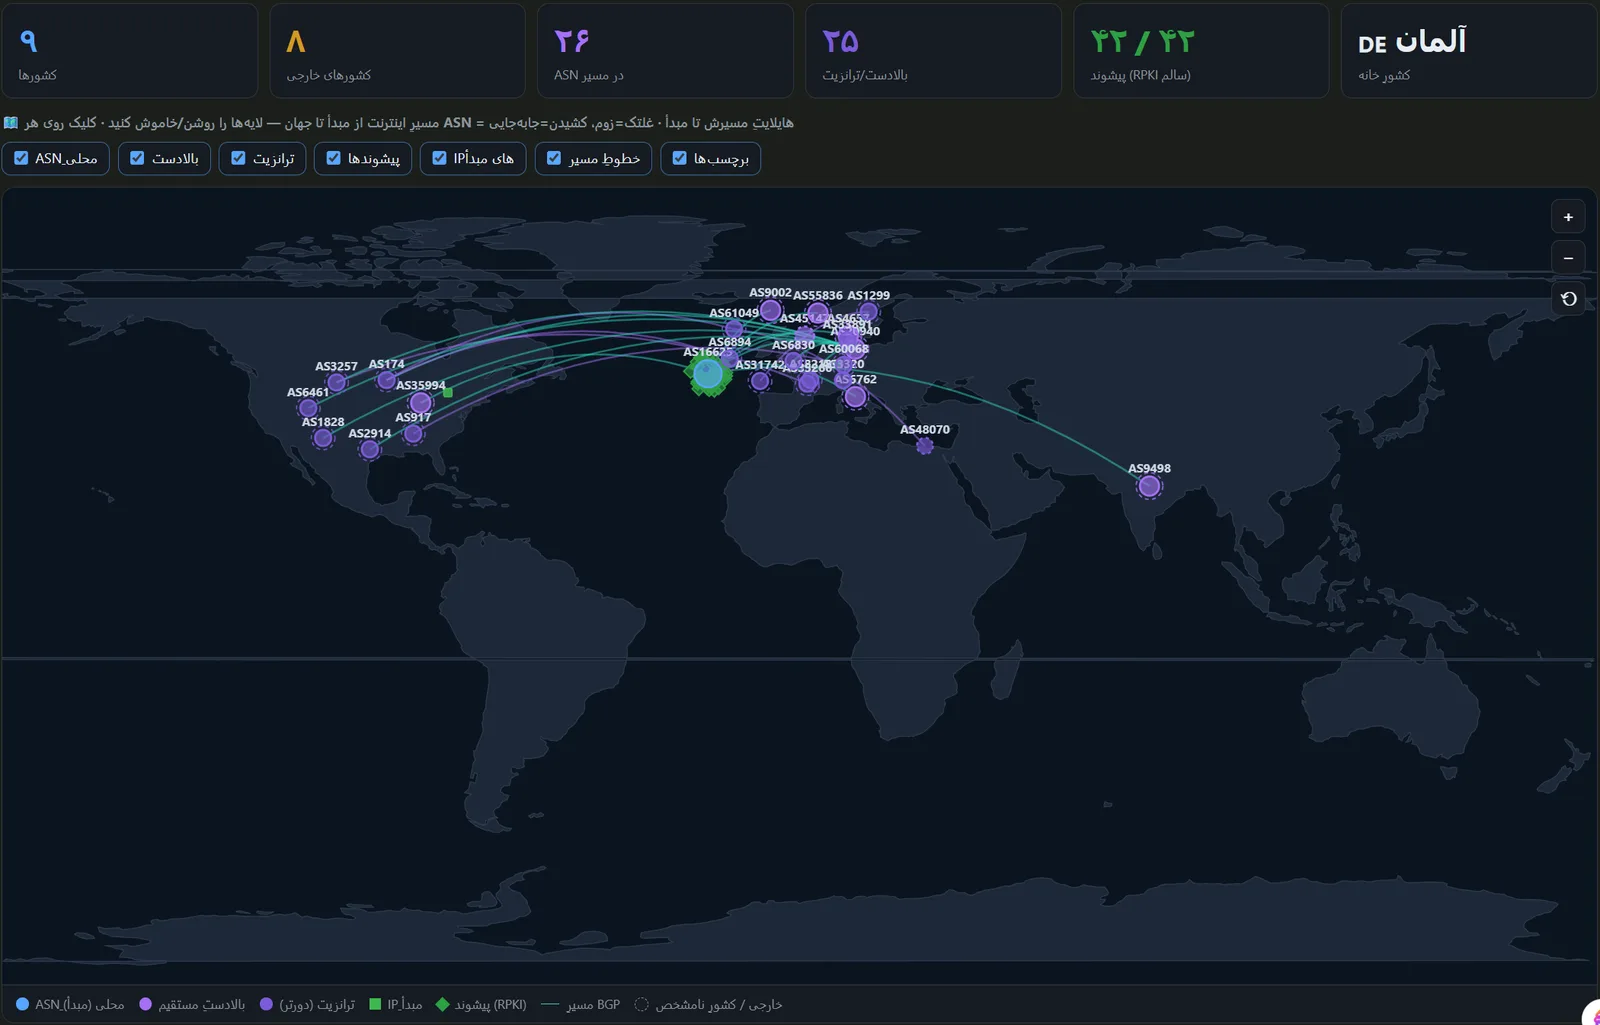
Global attack surface map
The network paths between the internet and your assets, with upstream providers, transit and RPKI status.
Asset relationship graph
Every domain, IP, network prefix, ASN and provider in one view, with the links between them.
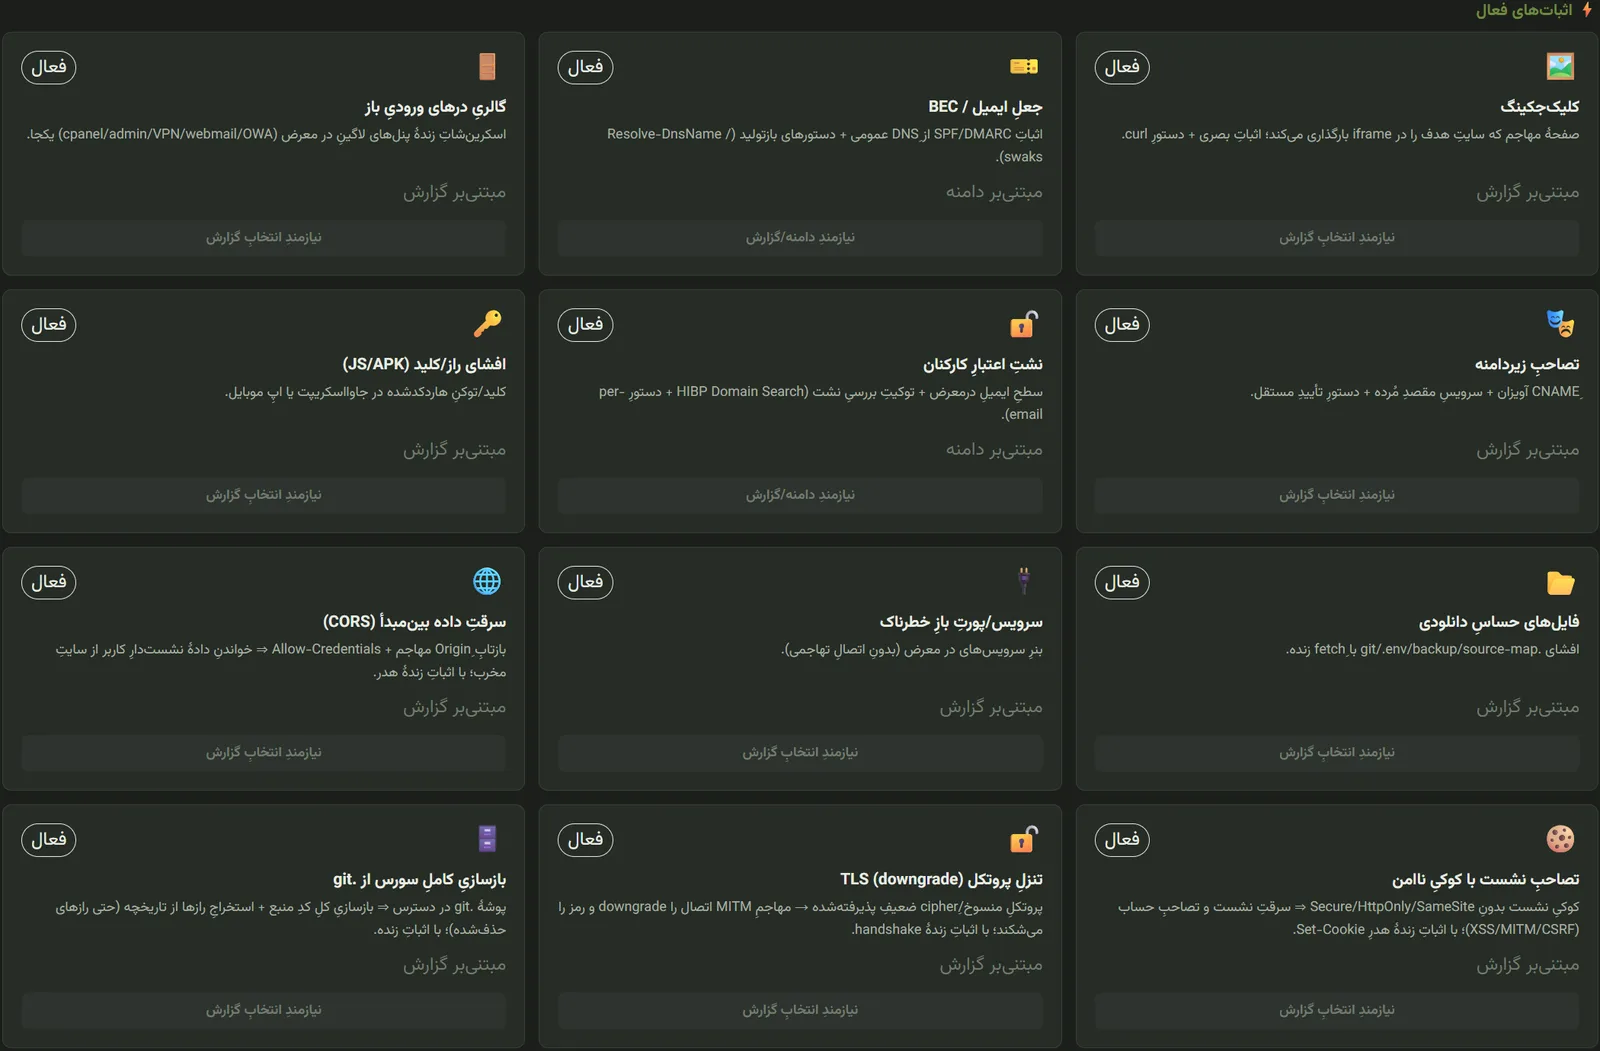
Proof-of-concept centre
Every weakness comes with a safe, reproducible proof your team can run.
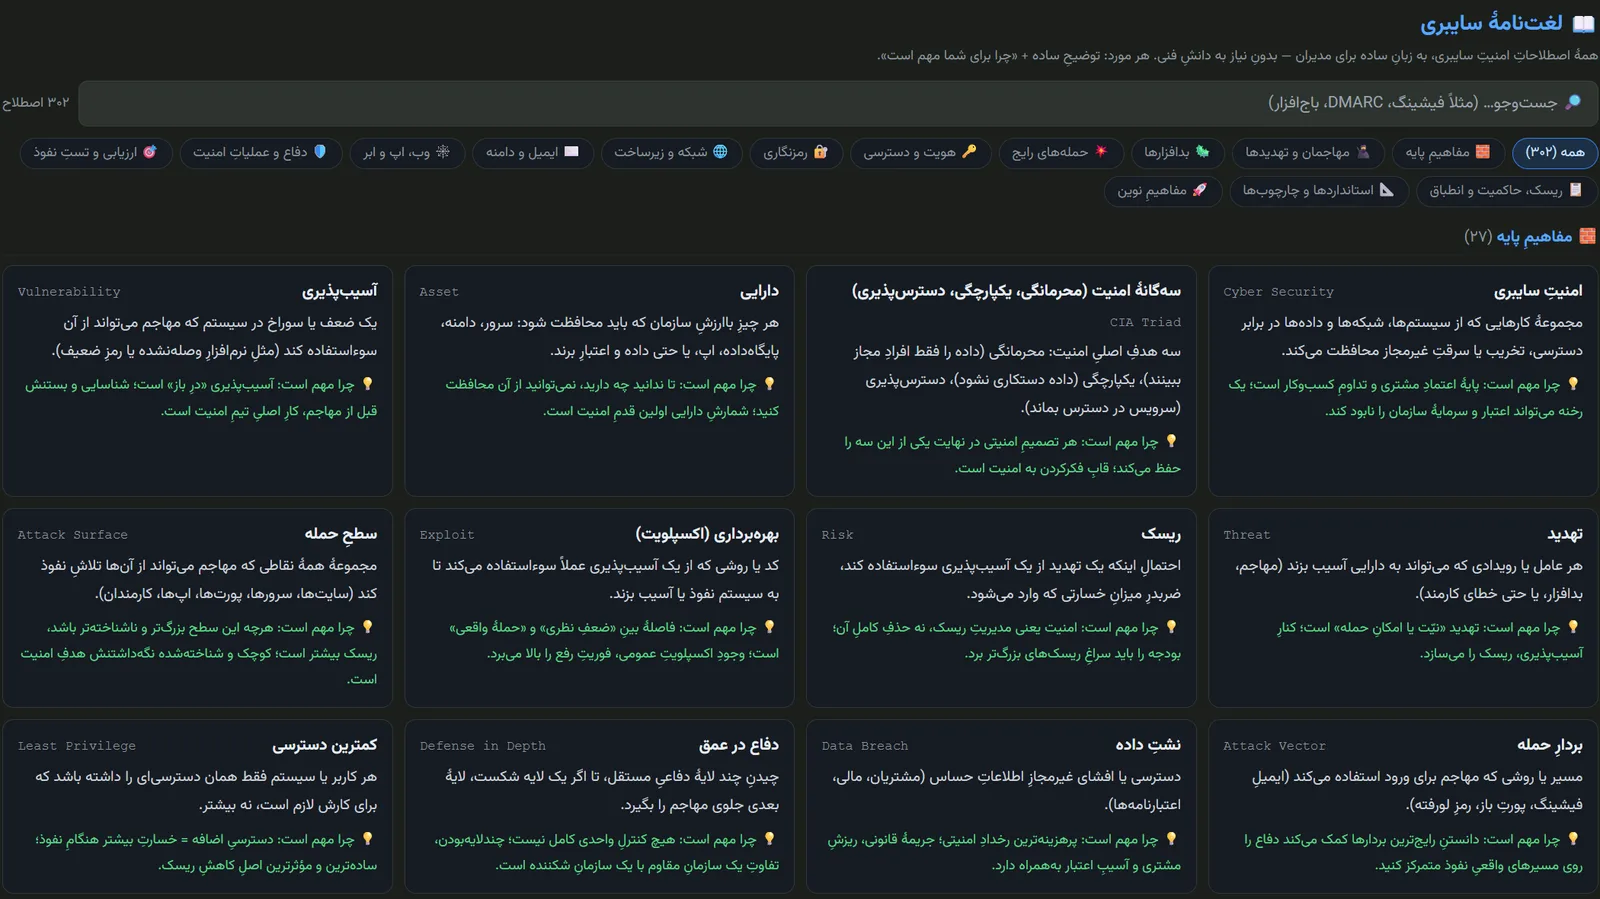
Cybersecurity glossary
More than 300 security terms in plain language, for executives and decision-makers.
From assessment to building security platforms
Alongside operating its own integrated platform, the STFC team designs and implements bespoke security solutions.
External Attack Surface Management (EASM)
Continuous discovery of your internet-facing assets (known, forgotten and shadow) and tracking of how they change over time.
- Complete map of domains, subdomains and IPs
- Forgotten assets and shadow IT identified
- Alerts on attack surface changes
Penetration testing & vulnerability assessment
Security assessment of web, network and infrastructure that combines automated testing with expert validation, without unproven claims.
Security platform design & development
Purpose-built monitoring, assessment and security management systems for organisations and critical infrastructure.
Infrastructure & routing analysis
Review of BGP data, RPKI status and how assets relate to network providers, to surface dependencies and concentrations of risk.
Attack chain analysis & simulation
Separate weaknesses combined into realistic adversary scenarios that show the cumulative business risk.
Mobile application security analysis
Static review of APK/XAPK packages to uncover exposed keys, misconfigurations and high-risk behaviour.
Independent contractor assessment
Measuring the security posture of IT suppliers and contractors, independently of the reports they provide themselves.
Advisory & technical deployment
Supporting your technical teams from the first assessment through remediation and stable deployment.
From asset discovery to final report, one continuous path
The platform runs, as a single automated workflow, steps that are usually scattered across several teams and tools.
- 01
Asset discovery
Domains, subdomains, IPs, ASNs, panels and internet-exposed services.
- 02
Evidence collection
Tests run in parallel across DNS, TLS, web, email and network layers.
- 03
Analysis & correlation
Findings are merged, de-duplicated, and confirmed evidence is separated from hypothesis.
- 04
Risk prioritisation
Weaknesses ranked by severity, exploitability and likely impact.
- 05
Multi-level reporting
Executive and technical output with reproducible evidence and remediation.
- 06
Continuous monitoring
Recurring assessments that track how the attack surface changes over time.
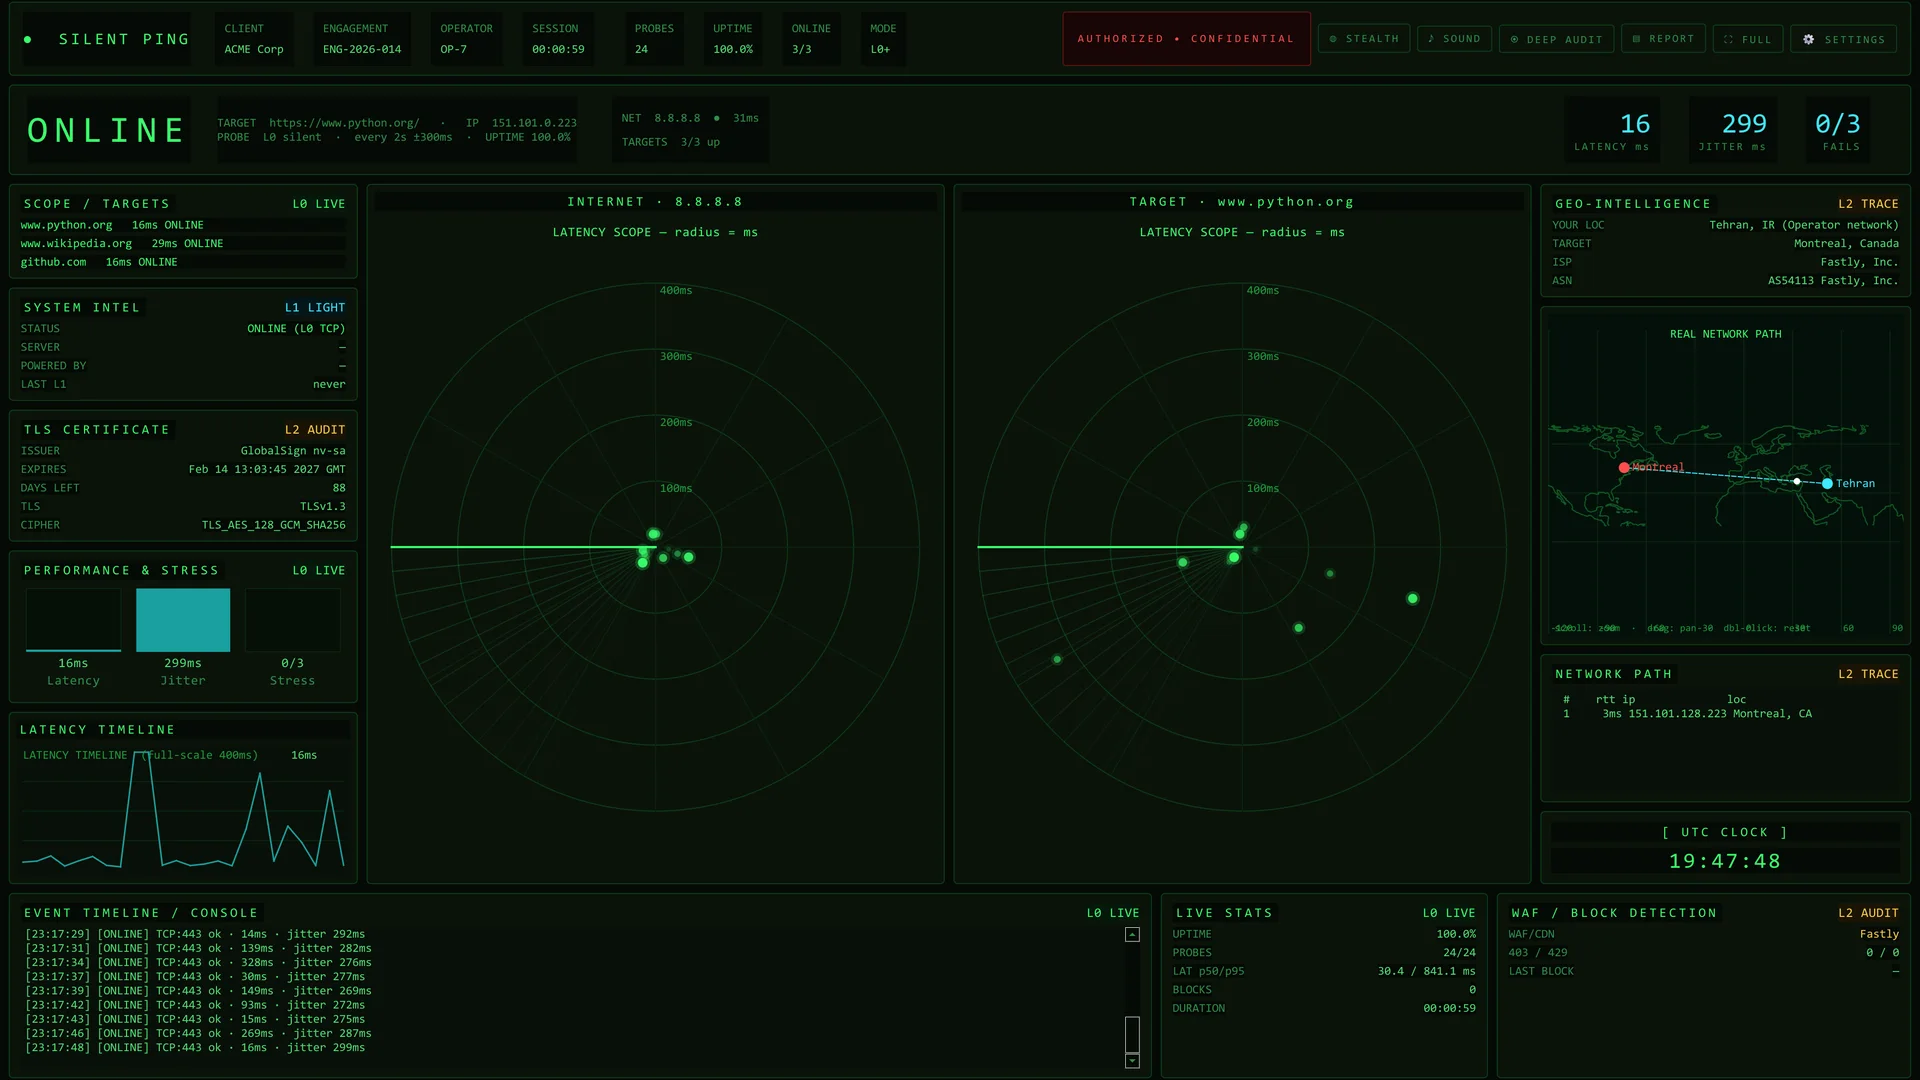
Silent Ping: know whether it is you or them
A console we wrote ourselves to replace Windows ping. It shows your link to the internet and your link to the target on two radars, and every probe is a single silent TCP handshake.
- Two radars: your internet and the target
- No request, no payload sent
- TLS and WAF audit and the real route on a map
See your infrastructure the way an adversary does
STFC · EASM Platform
What used to take months now runs in minutes
Conventional attack surface assessment is slow and costly because tools are fragmented and contractors are many. The platform removes that gap.
3+ months
Multiple specialists, separate tools, manual merging of results and report writing, at high expert cost, and with the risk of losing the links between scattered findings.
90 minutes
From first run to a multi-level report: confirmed evidence, risk prioritisation and an asset relationship map, in one integrated process that does not depend on a large team.
Overseeing the cybersecurity overseers
Companies and contractors responsible for protecting infrastructure or providing IT services to sensitive organisations can themselves be exposed to misconfigurations and security flaws. The platform enables an independent assessment that does not rely on that contractor's own reports. Observing a weakness is not proof of compromise in itself, but it is an early signal for independent validation and corrective action.
Learn more
Ready to see the platform live?
In a short session, watch asset discovery, assessment and report generation run against a sample domain.